
 Azerbaijan
 Bosnia and Herzegovina
 Bulgaria
 Croatia
 Czech Republic
 Denmark
 Estonia
 Finland
 Georgia
 Hungary
 Kazakhstan
 Kyrgyzstan
 Latvia
 Lithuania
 Moldova
 Montenegro
 North Macedonia
 Norway
 Poland
 Romania
 Serbia
 Slovakia
 Slovenia
 Sweden
 Tajikistan
 Turkmenistan
 Ukraine
 Uzbekistan

About the Webinar
AI accelerates development, but at the same time, teams receive more code that requires security checks. In this webinar with Secure Code Warrior, we will break down the risks of AI-assisted development, the skills needed to identify vulnerabilities, and ways to measure team progress.
During the event, we will discuss:
▪︎ Who is responsible for the security of AI-generated code?
▪︎ How do the risks of AI assistants differ from those of autonomous agents?
▪︎ Is your team ready to allocate resources for finding vulnerabilities in such code?
▪︎ How do you combine security checks, training, and skill assessments?
▪︎ How do you launch a secure development program with measurable results?
Agenda
AI writes code. Who verifies its security?
– A brief survey on AI usage in software development.
– How the responsibilities of the developer, team lead, and AppSec team are shifting.
– Introduction to Secure Code Warrior.
– Five questions about AI-driven development security that every team should answer.
From prompts to autonomous agents: How risks are evolving
– The difference between AI assistance and delegating tasks to agents.
– Shadow AI tools, unsafe changes, and gaps in code review.
– What companies should know about AI adoption within their teams.
Is your team ready to review AI-generated code?
– Skills required to review code for security flaws.
– Linking code review findings to targeted training.
– The role of SCW Learning, Trust Score, and Trust Agent in this process.
The Secure Code Warrior Solution: Platform capabilities
– Gamification and team tournaments.
– Hands-on exercises with code and OWASP Top 10 topics.
– Role-tailored training for Developers, DevOps, QA, and Security Specialists.
– Integrations with Jira, GitHub/GitLab, and CI/CD pipelines.
– Training and reporting for security and auditing needs.
– AI security exercises and skill assessment via Trust Score.
Demonstration
– Walking through a training exercise.
– Developer and manager dashboards.
– Metrics and reports for the CISO.
– An example of reviewing an insecure code snippet suggested by AI.
How to launch a program and evaluate results
– Selecting a pilot team, baseline skill assessment, and training focused on current team challenges.
– Key benchmark metrics: skill progression, vulnerability recurrence rate, and time to remediation.
– A relevant customer case study.
Q&A and next steps
– Discussion of participant scenarios and options for a custom demo or pilot tailored to your team’s tech stack and requirements.
Key takeaways
Understanding how to assess AI development risks within your team.
Insight into the skills needed to review AI-generated code.
Familiarity with hands-on exercises and skill assessment capabilities in Secure Code Warrior.
Benchmarks and guidelines for launching a secure development program.
Speaker
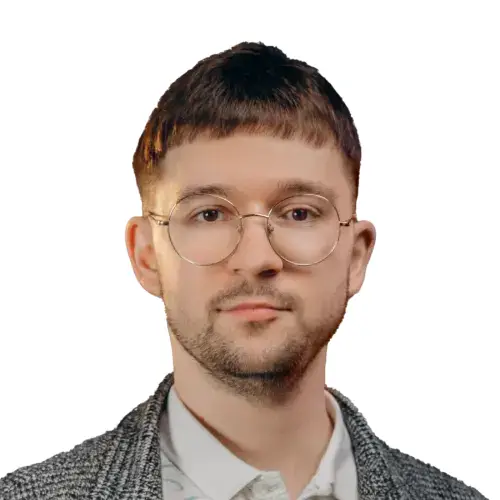
Yevhen Kurash
Sales Engineer, BAKOTECH
Yevhen has over 7 years of experience in cybersecurity, design, and implementation of IT information protection solutions. He specializes in Secure Software Development practices, fostering a secure coding culture, and raising cyber awareness among development teams. Combining expertise in penetration testing, automated security testing, and modeling real-world attack scenarios, he helps organizations integrate Secure by Design principles into their software development processes.
As a technical expert for Secure Code Warrior, Yevhen shares practical approaches to implementing developer training programs, building secure coding skills, and mitigating vulnerability risks right at the code-writing stage. His presentations combine hands-on experience, modern AppSec strategies, and real-world cases of building a secure SDLC.
To start
Registration