
 Azerbaijan
 Bosnia and Herzegovina
 Bulgaria
 Croatia
 Czech Republic
 Denmark
 Estonia
 Finland
 Georgia
 Hungary
 Kazakhstan
 Kyrgyzstan
 Latvia
 Lithuania
 Moldova
 Montenegro
 North Macedonia
 Norway
 Poland
 Romania
 Serbia
 Slovakia
 Slovenia
 Sweden
 Tajikistan
 Turkmenistan
 Ukraine
 Uzbekistan


About Nozomi Threat Intelligence
Nozomi Threat Intelligence is a continuously updated threat feed that empowers OT and IoT security teams to detect and mitigate emerging cyber risks. Backed by Nozomi Networks Labs, it enhances Guardian sensors with real-time data on known and zero-day vulnerabilities, malware signatures, and indicators of compromise.
Nozomi Threat Intelligence integrates seamlessly with Guardian, Vantage, and third-party security tools via industry-standard STIX/TAXII formats, ensuring comprehensive, up-to-date protection across critical infrastructure.
Nozomi Threat Intelligence Features
Advanced Threat and Anomaly Detection
Nozomi Threat Intelligence combines cutting-edge detection algorithms with tested rules to quickly identify threats and anomalies, minimizing false positives for more accurate results.
Comprehensive Threat Indicators
Access an extensive collection of threat indicators, including Yara rules, packet rules, STIX indicators, vulnerability signatures, and a constantly updated threat knowledge base to stay ahead of emerging risks.
Seamless Integration with Third-Party Solutions
The threat feed can be easily integrated with third-party security platforms such as firewalls and orchestration tools, supporting STIX format for broad compatibility and enhanced protection.
Prioritized Incident Response
Alerts are grouped by incidents for a consolidated view of network activity. Critical alerts are prioritized to help security teams take immediate action, minimizing disruption and ensuring faster remediation.
Nozomi Threat Intelligence Benefits
-

Industry-Leading Expertise
Benefit from Nozomi Networks Labs’ extensive research to identify and address the latest emerging threats and vulnerabilities in OT and IoT environments.
-
Accurate Threat Detection
Vendor’s rigorously tested rules ensure reliable detection while minimizing false positives, providing you with actionable insights and reducing alert fatigue.
-
Comprehensive Threat Coverage
Access an expansive list of threat indicators, ensuring that your security solution stays ahead of evolving risks with the most comprehensive and up-to-date intelligence available.
-
Seamless Third-Party Integration
Easily ingest threat feed into third-party security tools for enhanced protection, ensuring seamless integration and effective threat management across your entire security stack.
Тематичні ресурси
PRODUCT OVERVIEW | Threat Intelligence
Quickly Detect Threats to OT/IoT Systems andDefend Against Cyberattacks
OT & IoT SECURITY REPORT | EXECUTIVE SUMMARY
Assessing the Threat Landscape
What’s So Great About the Graph?
See how the Nozomi Networks graph provides a visual way to quickly manage your OT and IoT attack surface, including critical security alerts, traffic anomalies and networking issues.
News
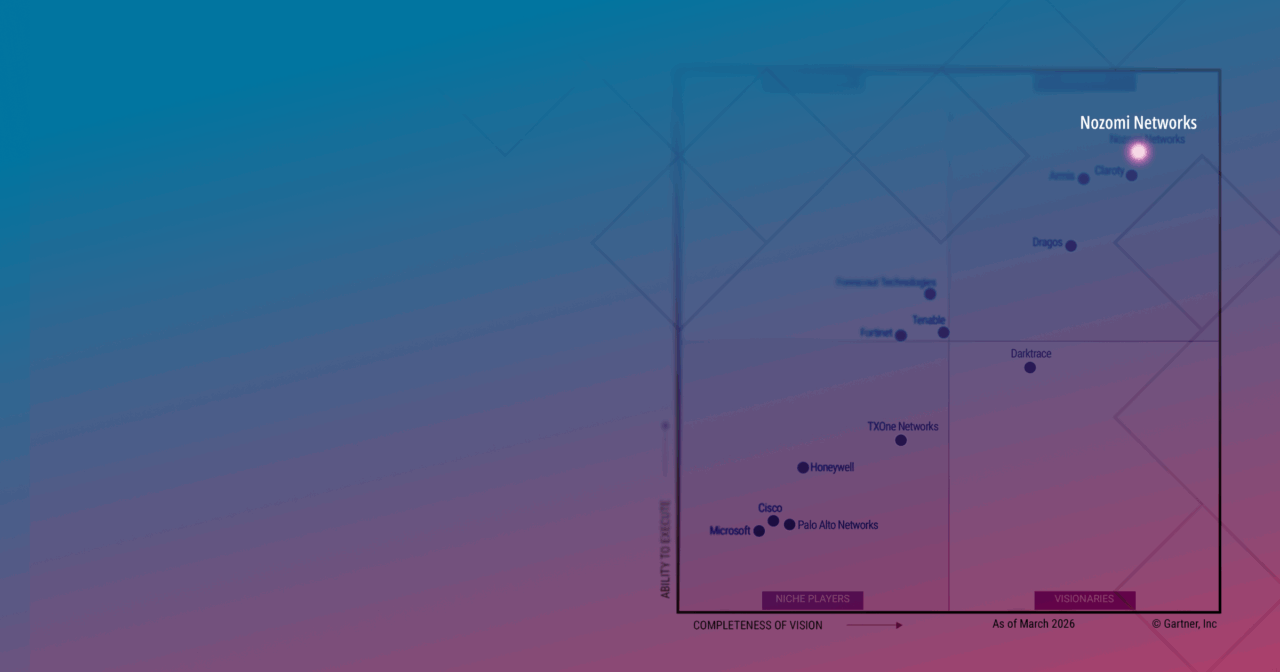
Nozomi Networks is a leader in the 2026 Gartner Magic Quadrant™! For the second year in a row, it tops the list for CPS security

BAKOTECH Awarded Emerging Markets Partner of the Year by Nozomi Networks
Continuous monitoring of OT networks: an investment in cybersecurity or an illusion of control?
Introducing OT & IoT security solutions to the Baltic market - BAKOTECH expands partnership with Nozomi Networks
Nozomi Networks and Skybox Security partner to mitigate the risks of converged IT/OT networks
Order a consultation